Developer Tools
XCIM Protocol
Experimental protocol for verified consent and permission evidence in email communications
- 0community votes
- 11DR by Ahrefs −1 (down) since last check
Ahrefs Domain Rating listed 19 Nov 2026, relisted 14 Nov 2026.
An experimental Internet-Draft protocol for establishing and verifying email recipient consent using EVP, OAuth or OIDC identity evidence, with portable
What it is
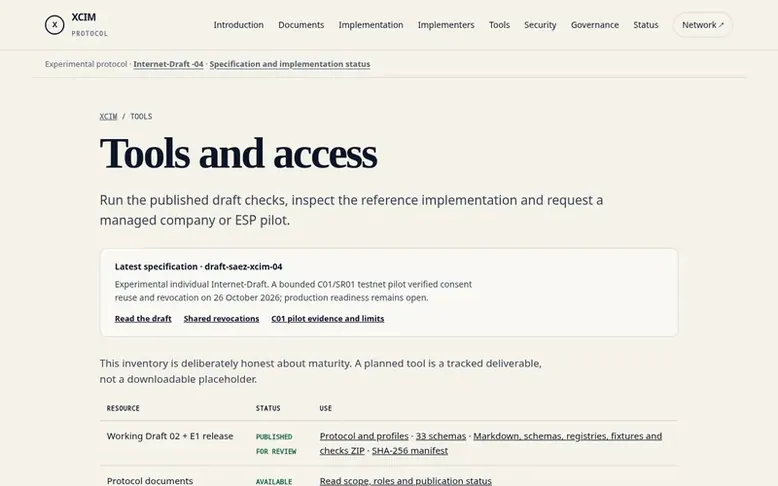
XCIM Protocol: the homepage
XCIM is an experimental individual Internet-Draft protocol published as draft-saez-xcim-04. It provides mechanisms for establishing and recording email recipient consent to identified senders for specific communication purposes, using verified address-control evidence from EVP, OAuth, or OIDC. The protocol maintains portable permission state and supports shared revocation synchronization through the SR01 path and individual signed-status requirements through the C01 path.
The project currently offers public tools including draft specification documents, reference implementation sources, Python and Node conformance runners, test vectors, JSON schemas, and managed pilot access for companies and email service providers. A bounded testnet pilot on Polygon Amoy verified consent reuse and revocation functionality on 26 October 2026, though production readiness remains open.
XCIM is distinct from email authentication mechanisms like SPF, DKIM and DMARC, which authenticate sending infrastructure rather than recipient consent. It complements email verification protocols like EVP by adding explicit permission recording beyond address-control verification. The protocol is coordinated by We Are 14 Inc. during Phase 0 and operates Emabled as a managed reference issuer.
Listed capabilities
- EVP, OAuth and OIDC identity verification methods
- Portable permission state records
- Shared revocation synchronization (SR01 path)
- Individual signed-status requirements (C01 path)
- Managed company and ESP consent evaluation pilots
- Reference implementation repository with ADRs
- Testnet proof sets and signed manifests
Follow XCIM Protocol for an email about each milestone, update and new product they post, in a daily summary.
XCIM Protocol metrics
| Metric | Value |
|---|---|
| Domain Rating | 11 −1 (down) since last check |
| Trust Flow | 2 no change since last check |
| Citation Flow | 20 no change since last check |
| Referring domains | 6 no change since last check |
| External backlinks | 53 no change since last check |
Ahrefs Domain Rating listed 19 Nov 2026, relisted 14 Nov 2026. Listed under topic: Society/People (2). Majestic listed 12 Nov 2026, relisted 12 Nov 2026. Link data listed by Majestic. Trust Flow, Citation Flow and Topical Trust Flow are trademarks of Majestic-12 Ltd.
XCIM Protocol domain listing data
Show the listing data
| Domain age | 3 months |
|---|---|
| Registered | |
| Expires | |
| Registrar | Squarespace Domains II LLC |
| DNSSEC | Signed |
XCIM Protocol launch receipt entry
| Measure | At launch, then latest |
|---|---|
| Domain Rating (Ahrefs) | 12 to 11 −1 (down) since launch 12 Nov 2026, then 19 Nov 2026 |
| Trust Flow (Majestic) | 2 first measured 12 Nov 2026 |
| Referring domains (Majestic) | 6 first measured 12 Nov 2026 |
Day 7 since launch. Next receipt: day 30, 12 Dec 2026. We show what changed, not what caused it: many things affect these numbers. Nothing here is estimated.
Before you launch
The playbook on SaaS Directory List lists what to prepare, what to post on launch day and where else to list your product.
Compare and explore
Quick answers
Can XCIM use EVP, OAuth or OIDC?
Yes. XCIM specifies three alternative methods to establish email address control giving consent. The issuer can use EVP verification, OAuth with provider API verification returning the verified email of the authorizing account, or OIDC as the identity-evidence profile. Each method requires its own signature, account, origin, session and freshness checks.
Does EVP verification mean the user accepted marketing?
No. Email-address verification through EVP is not communication permission. Marketing, newsletter, promotional and other optional purposes require an explicit XCIM decision against a defined Consent Manifest.
Does XCIM replace SPF, DKIM, or DMARC?
No. SPF, DKIM and DMARC continue to authenticate sending infrastructure and domains. XCIM explores evidence about explicit recipient consent to an identified sender for specified communication types, which is distinct from sender authentication.
Can an ESP evaluate a company's list using XCIM?
Yes, in the Emabled managed pilot. The company grants a revocable authorization scoped to its application, communication purpose and sending domain. The ESP uses its MFA-protected workspace for CSV/ZIP uploads, results and exports. Results concern permission and provenance, not mailbox existence or deliverability.
Does a recipient's consent expire after 300 seconds?
No. The original grant has its own stated duration. The 300-second experimental bound concerns how recent the evidence of withdrawals must be. Refreshing it does not require the recipient to log in or consent again.
Leave a review for XCIM Protocol
No reviews listed for XCIM Protocol yet. List the first one.
Listing a review is free. No one pays for reviews. See the listed reviews
List reviews · List updates · Share the list · Your tool? Claim this list entry · Report this list entry
XCIM Protocol has a free listing. The owner can unlock the full profile with a paid launch for $5:
- Founder story (locked)
- Milestones (locked)
- Demo video (locked)
- Dofollow website link: not on this free listing (its website link is nofollow)
Also on the list
-
DR 76 no change since last check 8 votes. Log in to move Remotion up the list
-
 Number 2: IT Admin Utils
Browser-based diagnostic tools for understanding systemd, Docker, DNS, cURL, and SSH errors
Developer ToolsNew ZealandVerified
DR 2 no change since last check 3 votes. Log in to move IT Admin Utils up the list -
DR 39 +1 (up) since last check 1 votes. Log in to move NerimaSoft up the list
-
 Number 4: Laravel Suspicious Login
Detect and respond to suspicious logins in Laravel applications
Developer ToolsBelgiumSince 2004
DR 74 no change since last check 0 votes. Log in to move Laravel Suspicious Login up the list