Developer Tools
Laravel Suspicious Login
Detect and respond to suspicious logins in Laravel applications
- 0community votes
- 74DR by Ahrefs no change since last check
- 2004founded
Ahrefs Domain Rating listed 19 Nov 2026, relisted 19 Nov 2026.
An open source Laravel package that scores logins based on device, location and account history to detect suspicious activity and notify users or block
What it is
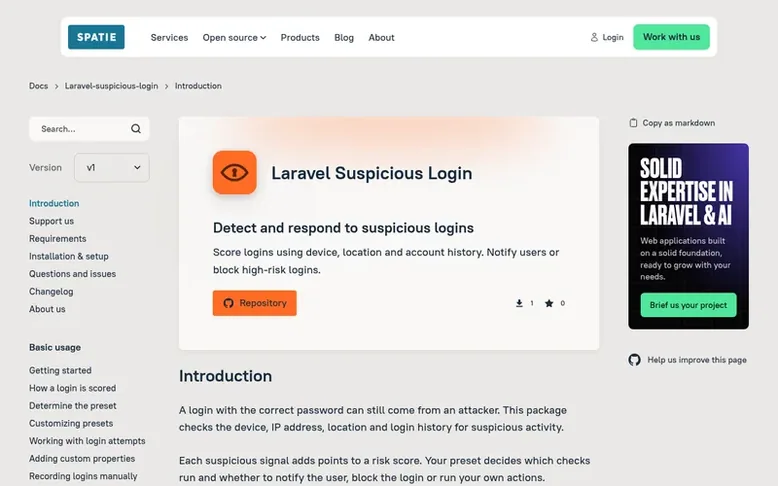
Laravel Suspicious Login: the homepage
Laravel Suspicious Login is an open source package for Laravel that helps detect and respond to suspicious user logins. It scores login attempts by analyzing device information, IP address, geographic location, and account login history to identify potentially risky authentication events.
The package runs multiple security checks on each login attempt, with each suspicious signal adding points to a risk score. The risk score determines whether the system should notify the user, block the login, or take other custom actions. It includes preset configurations for common use cases and allows developers to create custom presets with specific thresholds and actions.
The package integrates with Laravel's login events, making it compatible with popular Laravel authentication packages like Breeze, Jetstream, and Fortify. It features replaceable components including checks, actions, and drivers, and provides event hooks for custom handling of login attempts.
Listed capabilities
- Risk scoring based on device, location, and login history
- New device detection
- New IP address detection
- Geographic location checking
- Impossible travel detection
- IP reputation checking
- Failed attempt tracking
- Credential stuffing detection
- User notifications for suspicious logins
- Login blocking for high-risk attempts
Pricing
Pricing model: Open source
Follow Laravel Suspicious Login for an email about each milestone, update and new product they post, in a daily summary.
Laravel Suspicious Login metrics
| Metric | Value |
|---|---|
| Domain Rating | 74 no change since last check |
| Trust Flow | 17 no change since last check |
| Citation Flow | 47 no change since last check |
| Referring domains | 1,613 no change since last check |
| External backlinks | 68,576 no change since last check |
Ahrefs Domain Rating listed 19 Nov 2026, relisted 19 Nov 2026. Listed under topic: Arts/Visual Arts (16). Majestic listed 19 Nov 2026, relisted 19 Nov 2026. Link data listed by Majestic. Trust Flow, Citation Flow and Topical Trust Flow are trademarks of Majestic-12 Ltd.
Laravel Suspicious Login domain listing data
Show the listing data
.be is run by a registry that does not publish RDAP data: there is no public record for us to show.
Laravel Suspicious Login launch receipt entry
| Measure | At launch, then latest |
|---|---|
| Domain Rating (Ahrefs) | 74 first measured 19 Nov 2026 |
| Trust Flow (Majestic) | 17 first measured 19 Nov 2026 |
| Referring domains (Majestic) | 1,613 first measured 19 Nov 2026 |
Day 0 since launch. Next receipt: day 30, 19 Dec 2026. We show what changed, not what caused it: many things affect these numbers. Nothing here is estimated.
Before you launch
The playbook on SaaS Directory List lists what to prepare, what to post on launch day and where else to list your product.
Compare and explore
Quick answers
How does the package score login risk?
The package analyzes multiple factors including device history, IP address changes, geographic location, and login patterns. Each suspicious signal adds points to a risk score. For example, a login from a new device adds 25 points, from a new IP address adds 10 points, and from a new country adds 30 points. The score determines the risk level and corresponding actions.
What actions can the package take on suspicious logins?
The package can notify users about suspicious login attempts via email or take blocking actions to prevent high-risk logins. You can configure custom actions through presets, and the package provides event hooks to run your own custom logic in response to login attempts.
How does the package integrate with Laravel authentication?
The package listens for Laravel's login events, making it compatible with Breeze, Jetstream, Fortify, and custom session login controllers. No special configuration is required as it hooks into Laravel's standard authentication system.
Leave a review for Laravel Suspicious Login
No reviews listed for Laravel Suspicious Login yet. List the first one.
Listing a review is free. No one pays for reviews. See the listed reviews
List reviews · List updates · Share the list · Your tool? Claim this list entry · Report this list entry
Laravel Suspicious Login has a free listing. The owner can unlock the full profile with a paid launch for $5:
- Founder story (locked)
- Milestones (locked)
- Demo video (locked)
- Dofollow website link: not on this free listing (its website link is nofollow)
Also on the list
-
DR 76 no change since last check 8 votes. Log in to move Remotion up the list
-
 Number 2: IT Admin Utils
Browser-based diagnostic tools for understanding systemd, Docker, DNS, cURL, and SSH errors
Developer ToolsNew ZealandVerified
DR 2 no change since last check 3 votes. Log in to move IT Admin Utils up the list -
DR 39 +1 (up) since last check 1 votes. Log in to move NerimaSoft up the list
-
 Number 4: AWP Validator
Validate Agentic Workflow Protocol manifests in your browser with YAML rules, JSON Schema and semantic checks
DR 1 no change since last check 0 votes. Log in to move AWP Validator up the list