
Cybersecurity
PlugLeak
Free security check for AI-built apps
- 0community votes
- 2DR by Ahrefs +1 (up) since last check
Ahrefs Domain Rating listed 6 Nov 2026, relisted 4 Nov 2026.
Automated passive security scanner that checks AI-built apps for leaked API keys, Supabase secrets, exposed .env/.git files and missing security headers in
What it is
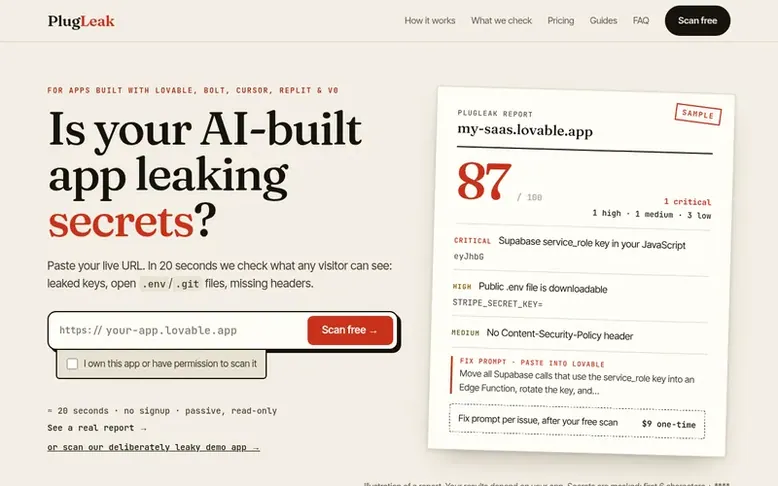
PlugLeak: the homepage
PlugLeak is a free automated security scanner designed for apps built with AI tools like Lovable, Bolt, Cursor, Replit and v0. It performs a passive 20-second scan of your live app by checking what any visitor's browser can see: leaked API keys, Supabase service_role keys, exposed .env and .git/config files, and missing security headers.
The scanner makes only GET requests, never logging in, submitting forms, querying databases or testing Row Level Security policies. It checks for critical secrets from Stripe, OpenAI, Anthropic, AWS, GitHub, Supabase and PEM private keys, plus verifies HTTPS configuration and SSL certificate validity.
The free scan shows your security score out of 100 immediately. To see the full problem list, you provide an email. For $9 one-time, you can unlock copy-paste fix prompts written for your AI builder (Lovable, Bolt or Cursor) that include what to rotate and how to verify the fix. A $29 pack includes 10 fix reports for re-scanning after each deploy.
PlugLeak masks all found secrets on the spot (first 6 characters + ****) and never stores full secrets. It is built to be safe to run on production apps and is honest about its scope: it catches common public leaks but is not a full security audit.
Listed capabilities
- Scan live apps in about 20 seconds
- Detects Stripe, OpenAI, Anthropic and AWS keys
- Checks for exposed .env and .git files
- Validates security headers (CSP, HSTS, etc)
- Verifies HTTPS and SSL certificate validity
- Masks secrets in reports (first 6 chars + ****)
- No database queries or Row Level Security testing
- Copy-paste fix prompts for Lovable, Bolt, Cursor
Pricing
Pricing model: Freemium
Free scan: score out of 100. Fix report: $9 one-time for copy-paste fix prompts per issue. 10 fix reports: $29 one-time for 10 credits for re-scans.
Follow PlugLeak for an email about each milestone, update and new product they post, in a daily summary.
PlugLeak metrics
| Metric | Value |
|---|---|
| Domain Rating | 2 +1 (up) since last check |
| Trust Flow | 0 no change since last check |
| Citation Flow | 0 no change since last check |
| Referring domains | 0 no change since last check |
| External backlinks | 0 no change since last check |
Ahrefs Domain Rating listed 6 Nov 2026, relisted 4 Nov 2026. Majestic listed 31 Oct 2026, relisted 31 Oct 2026. Link data listed by Majestic. Trust Flow, Citation Flow and Topical Trust Flow are trademarks of Majestic-12 Ltd.
PlugLeak domain listing data
Show the listing data
| Domain age | 8 days |
|---|---|
| Registered | |
| Expires | |
| Registrar | Name.com, Inc. |
| DNSSEC | Not signed |
PlugLeak launch receipt entry
| Measure | At launch, then latest |
|---|---|
| Domain Rating (Ahrefs) | 0 to 2 +2 (up) since launch 31 Oct 2026, then 5 Nov 2026 |
| Trust Flow (Majestic) | 0 first measured 31 Oct 2026 |
| Referring domains (Majestic) | 0 first measured 31 Oct 2026 |
Day 5 since launch. Next receipt: day 30, 30 Nov 2026. We show what changed, not what caused it: many things affect these numbers. Nothing here is estimated.
Before you launch
The playbook on SaaS Directory List lists what to prepare, what to post on launch day and where else to list your product.
Compare and explore
Quick answers
Is it safe to scan my live app?
Yes. The free scan only makes the same GET requests any visitor's browser makes, plus one request each to /.env and /.git/config. It never logs in, submits forms, queries your database or tries to exploit anything.
Do you store my secrets?
No. Any key found is masked on the spot (first 6 characters + ****) before the report is saved. Full secrets are never stored.
What does the $9 Fix report include?
Every finding comes with a copy-paste prompt written for Lovable, Bolt or Cursor, so your AI builder can fix it for you — plus what to rotate and how to verify the fix.
Why does it ask for my email?
The score is free and instant. To see the full list of problems the scanner asks for an email so it can send you the report link and tell you when weekly monitoring launches. There is no spam and you can unsubscribe any time.
Is this a security audit?
No. It is an automated check of what your app exposes publicly. It catches common, costly mistakes fast, but it cannot prove your app is secure.
Leave a review for PlugLeak
No reviews listed for PlugLeak yet. List the first one.
Listing a review is free. No one pays for reviews. See the listed reviews
List reviews · List updates · Share the list · Your tool? Claim this list entry · Report this list entry
PlugLeak has a free listing. The owner can unlock the full profile with a paid launch for $5:
- Founder story (locked)
- Milestones (locked)
- Demo video (locked)
- Dofollow website link (locked)
Also on the list
-
 Number 1: KechX Technologies
Fraud analytics and intelligence company that analyzes, detects, and exposes fraud in real time
CybersecurityUnited StatesSince 2026
DR 0 no change since last check 0 votes. Log in to move KechX Technologies up the list -
 Number 2: InboxGuards
Account-takeover alarm for Google Workspace and Microsoft 365
CybersecurityUnited States
DR 31 no change since last check 0 votes. Log in to move InboxGuards up the list -
 Number 3: CyberDetails
Vulnerability intelligence platform with AI-assisted threat analysis and SIEM detection queries
CybersecuritySince 2019
DR 36 no change since last check 0 votes. Log in to move CyberDetails up the list -
 Number 4: Dynamo AI
End-to-end AI performance, security, and compliance solutions for enterprise-grade generative AI
CybersecurityUnited States
DR 51 no change since last check 0 votes. Log in to move Dynamo AI up the list